Дзвінок від «ІТ-підтримки» — і компанія в заручниках: керівник Нацполіції розповів про викриття хакерів, які отримали понад $40 млн
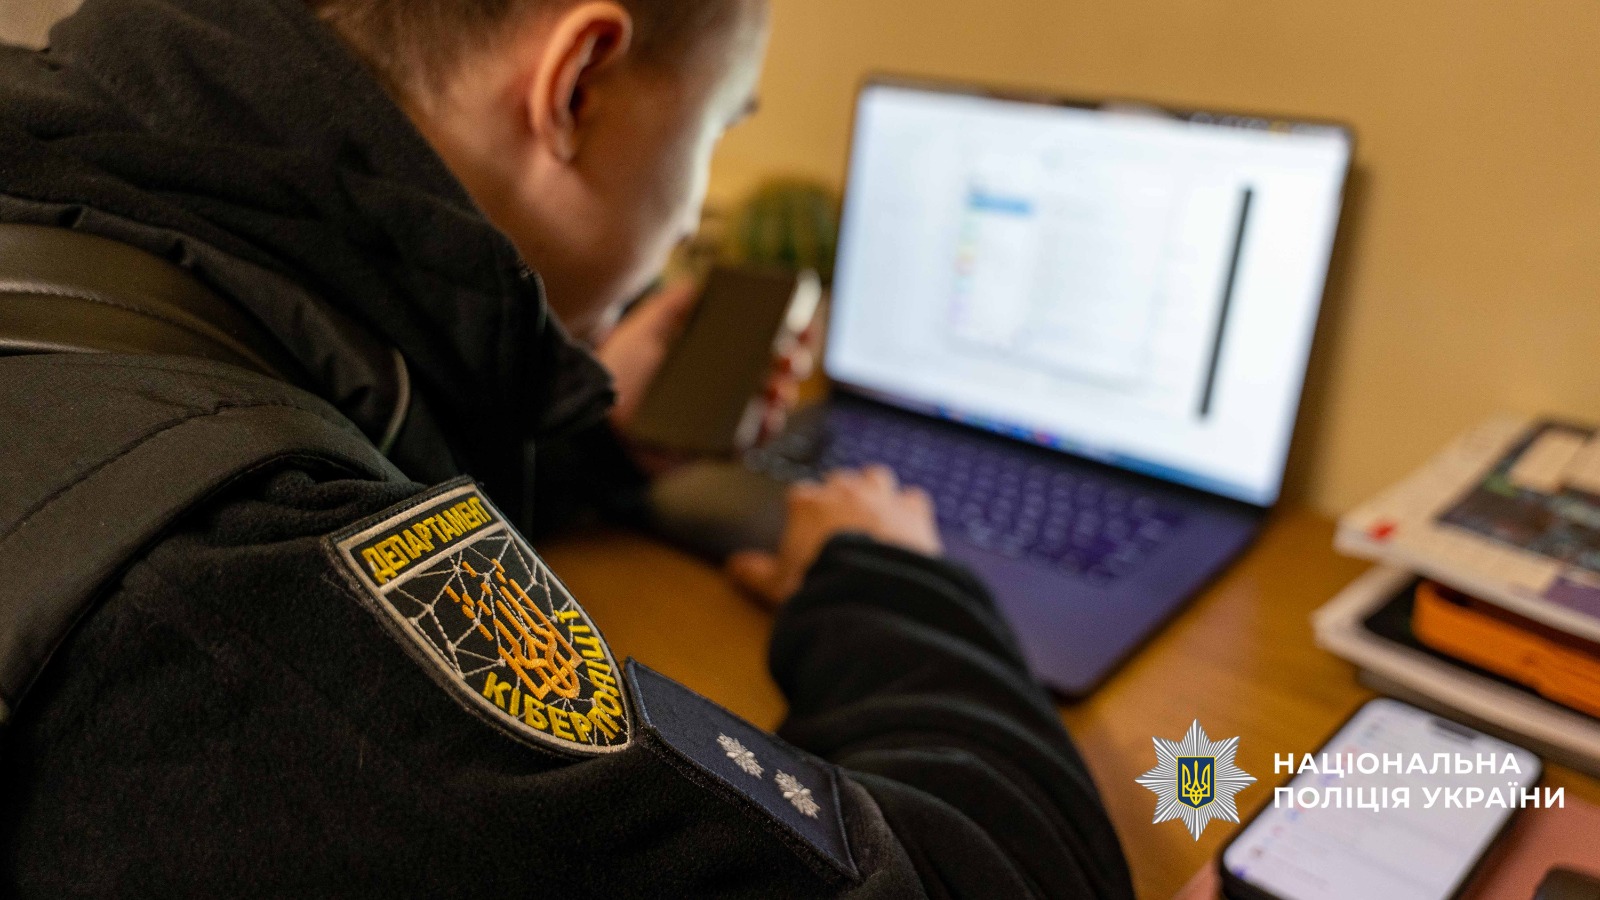
Працівник компанії говорив телефоном із нібито фахівцем ІТ-підтримки. Поки один зловмисник утримував його на лінії, інший входив до корпоративної системи. Розмову завершили лише після підтвердження успішного зламу. Це один із задокументованих епізодів діяльності міжнародного хакерського угруповання, яке викрадало дані, блокувало роботу підприємств і вимагало мільйонні викупи.
Подробиці спільного з ФБР розслідування в ексклюзивному коментарі Цензор.НЕТ розповів т.в.о. голови Національної поліції України Максим Цуцкірідзе. Серед потерпілих — американське підприємство, яке після атаки сплатило хакерам п’ять мільйонів доларів.
«З американського підприємства зловмисники викрали 1,4 терабайта даних і поширили атаку на інші підприємства тієї самої групи. Спочатку вимагали 10 мільйонів доларів. Після переговорів отримали п’ять мільйонів», — повідомив він.
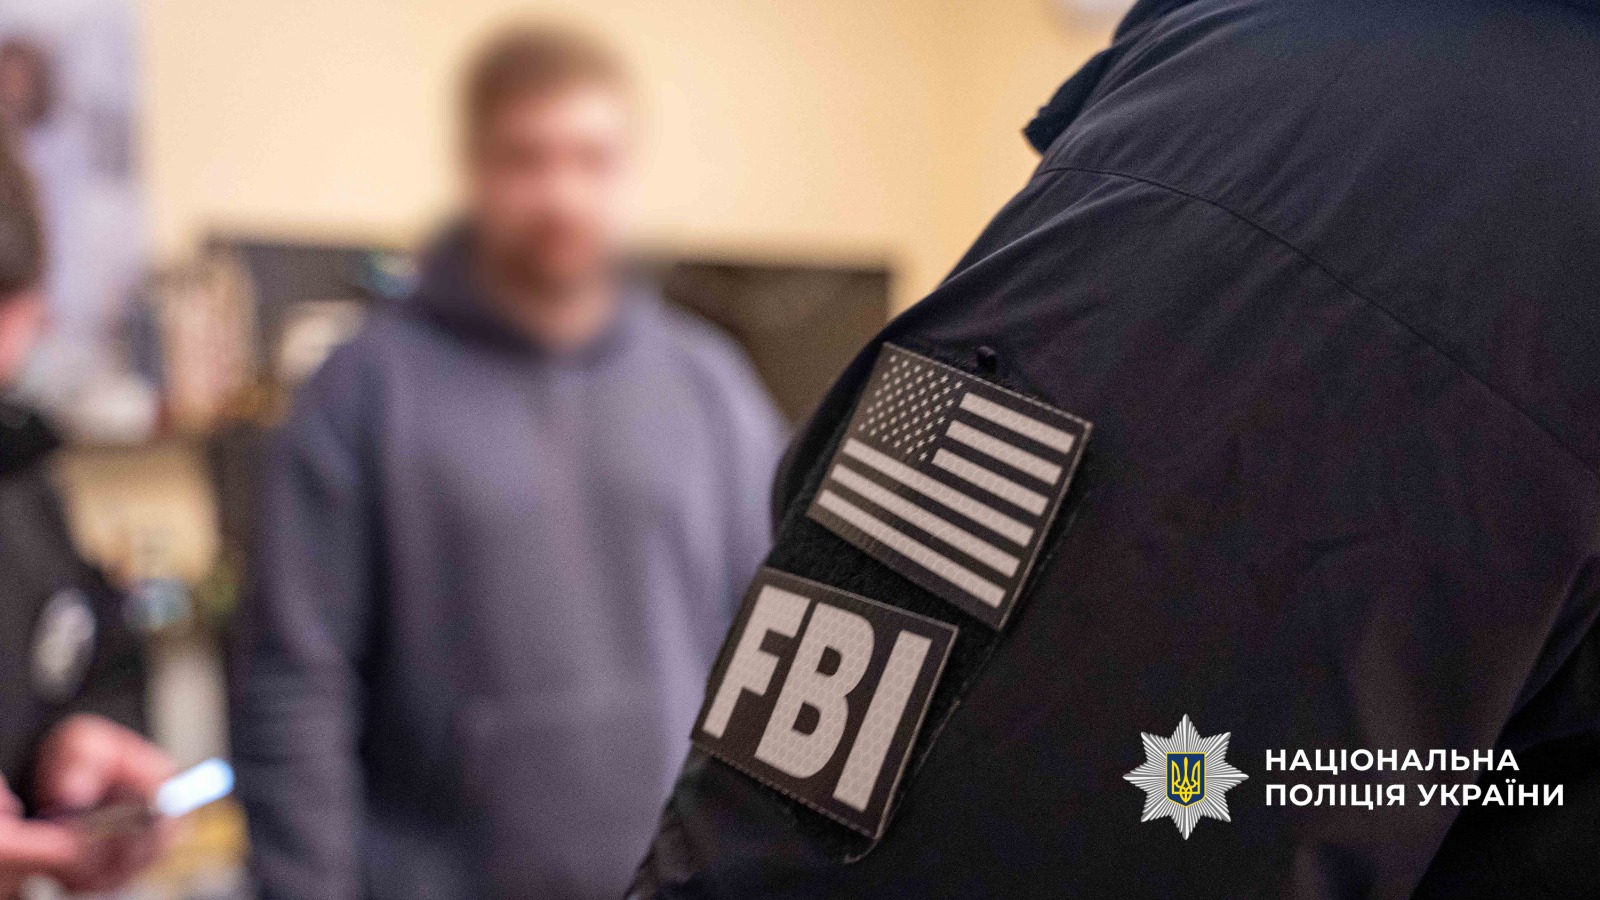
Діяльність організації понад два роки документували оперативники Департаменту кіберполіції та слідчі Головного слідчого управління спільно з Федеральним бюро розслідувань США.
«Ми встановили щонайменше 28 компаній, які перерахували хакерам понад 40,5 мільйона доларів викупу — близько 1,8 мільярда гривень в еквіваленті. Це вже сплачені гроші. Остаточний розмір збитків ще встановлюємо», — зазначив Цуцкірідзе.
За даними слідства, до організації входять щонайменше 27 осіб із різних країн, зокрема України, Казахстану та росії. Пов’язана з нею ширша злочинна структура налічує понад 60 учасників у восьми юрисдикціях. Серед них — колишні учасники відомого хакерського угруповання Conti.
Кожну атаку ретельно готували. Зловмисники вивчали фінансовий стан компанії, її активи, працівників та вразливості інформаційних систем. Цілями ставали підприємства нафтогазової, фармацевтичної, промислової та логістичної галузей, фінансові установи й об’єкти критичної інфраструктури.
Для проникнення в корпоративні мережі використовували обман працівників. За словами очільника Нацполіції, угруповання розробило власний інструмент для автоматизації таких контактів.
«Вони створили власну платформу з голосовими повідомленнями, згенерованими штучним інтелектом. Телефонували працівникам компаній, представлялися фахівцями ІТ-підтримки. Під приводом технічної допомоги переконували передати облікові дані або встановити програму віддаленого доступу. Так отримували доступ до корпоративної мережі», — розповів Цуцкірідзе.
Після проникнення хакери викрадали конфіденційну інформацію та шифрували файли, зокрема за допомогою програм-вимагачів. Робота компаній блокувалася.
«Компанію позбавляли доступу до власних даних, а потім вимагали мільйони за їх розшифрування. Одночасно погрожували оприлюднити викрадену інформацію. На потерпілих тиснули з обох боків, змушуючи платити викуп у криптовалюті», — пояснив він.
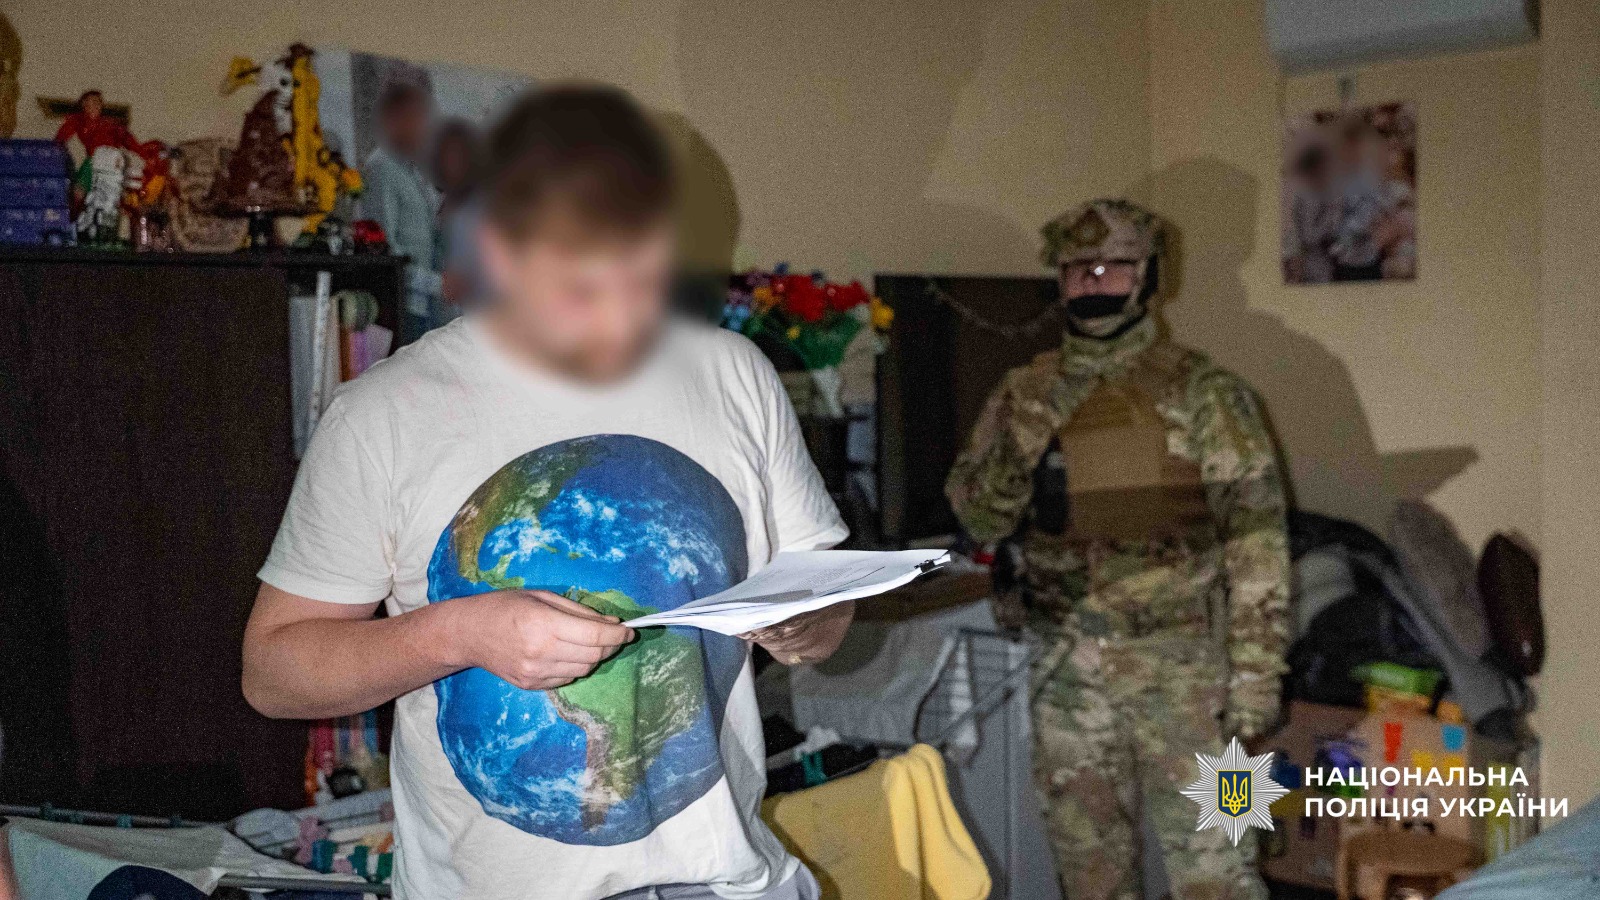
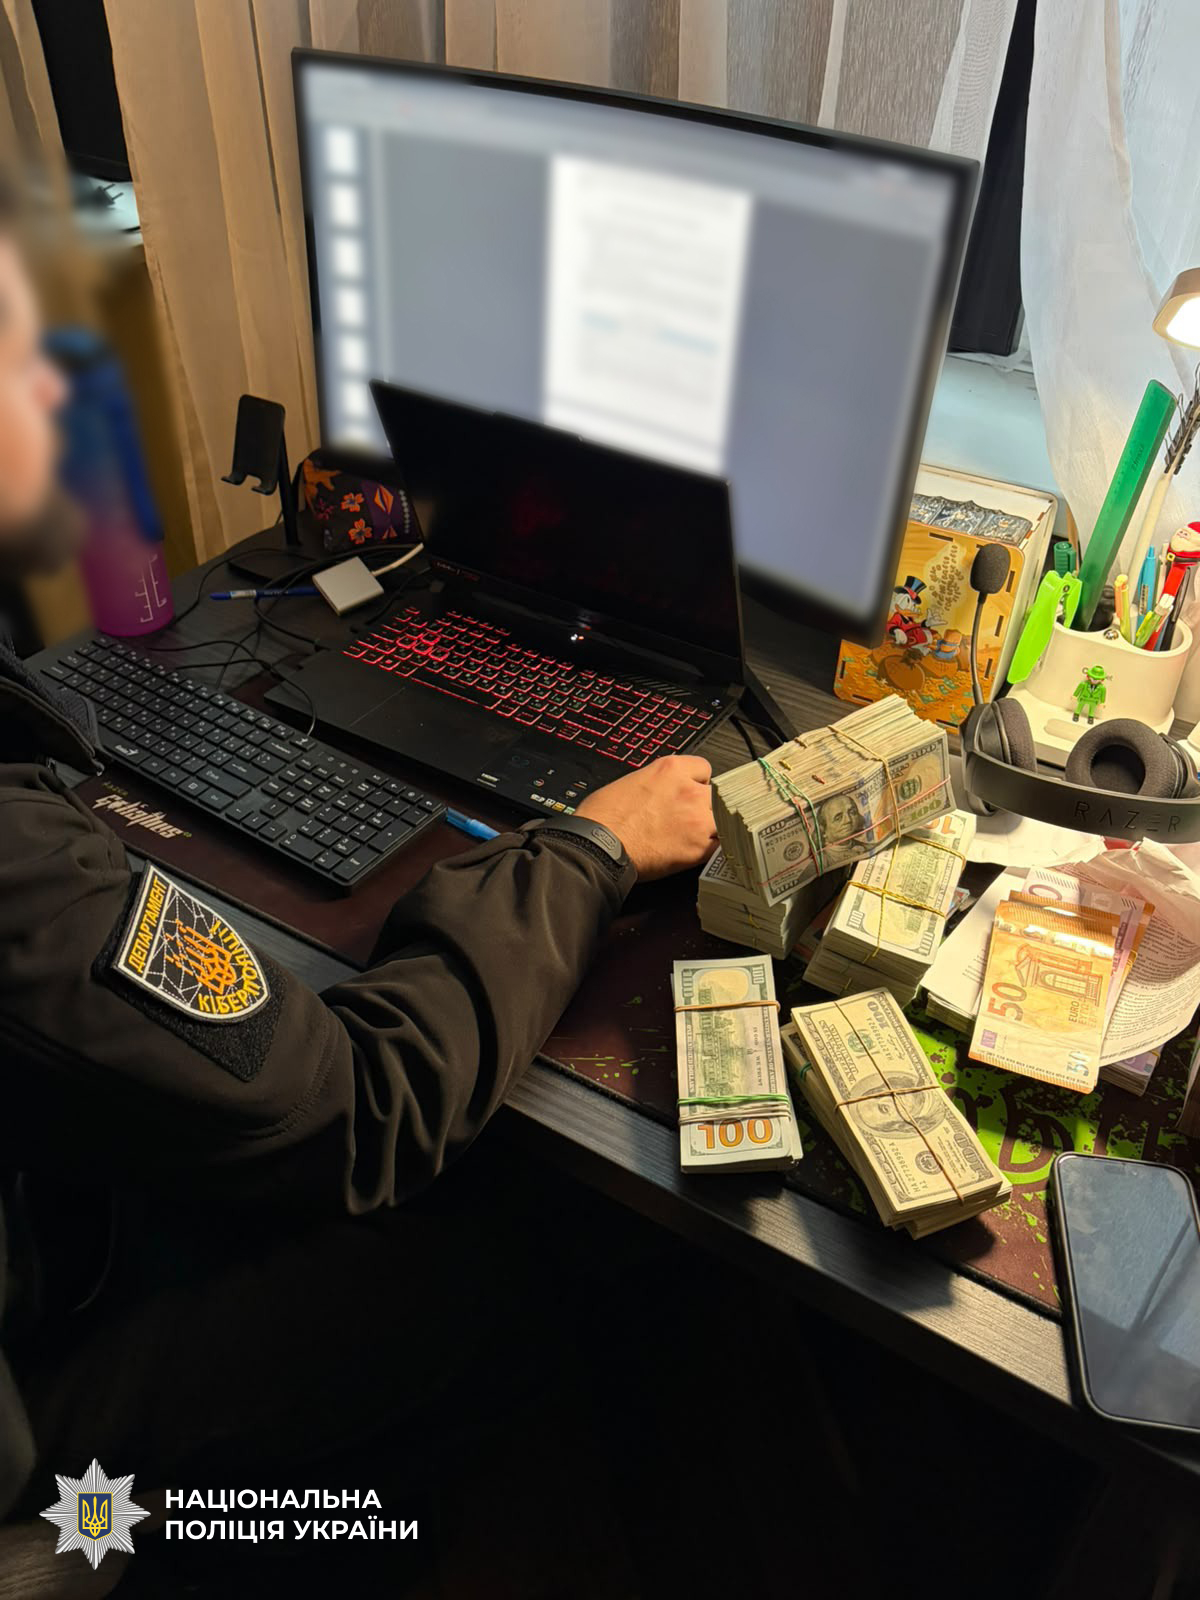
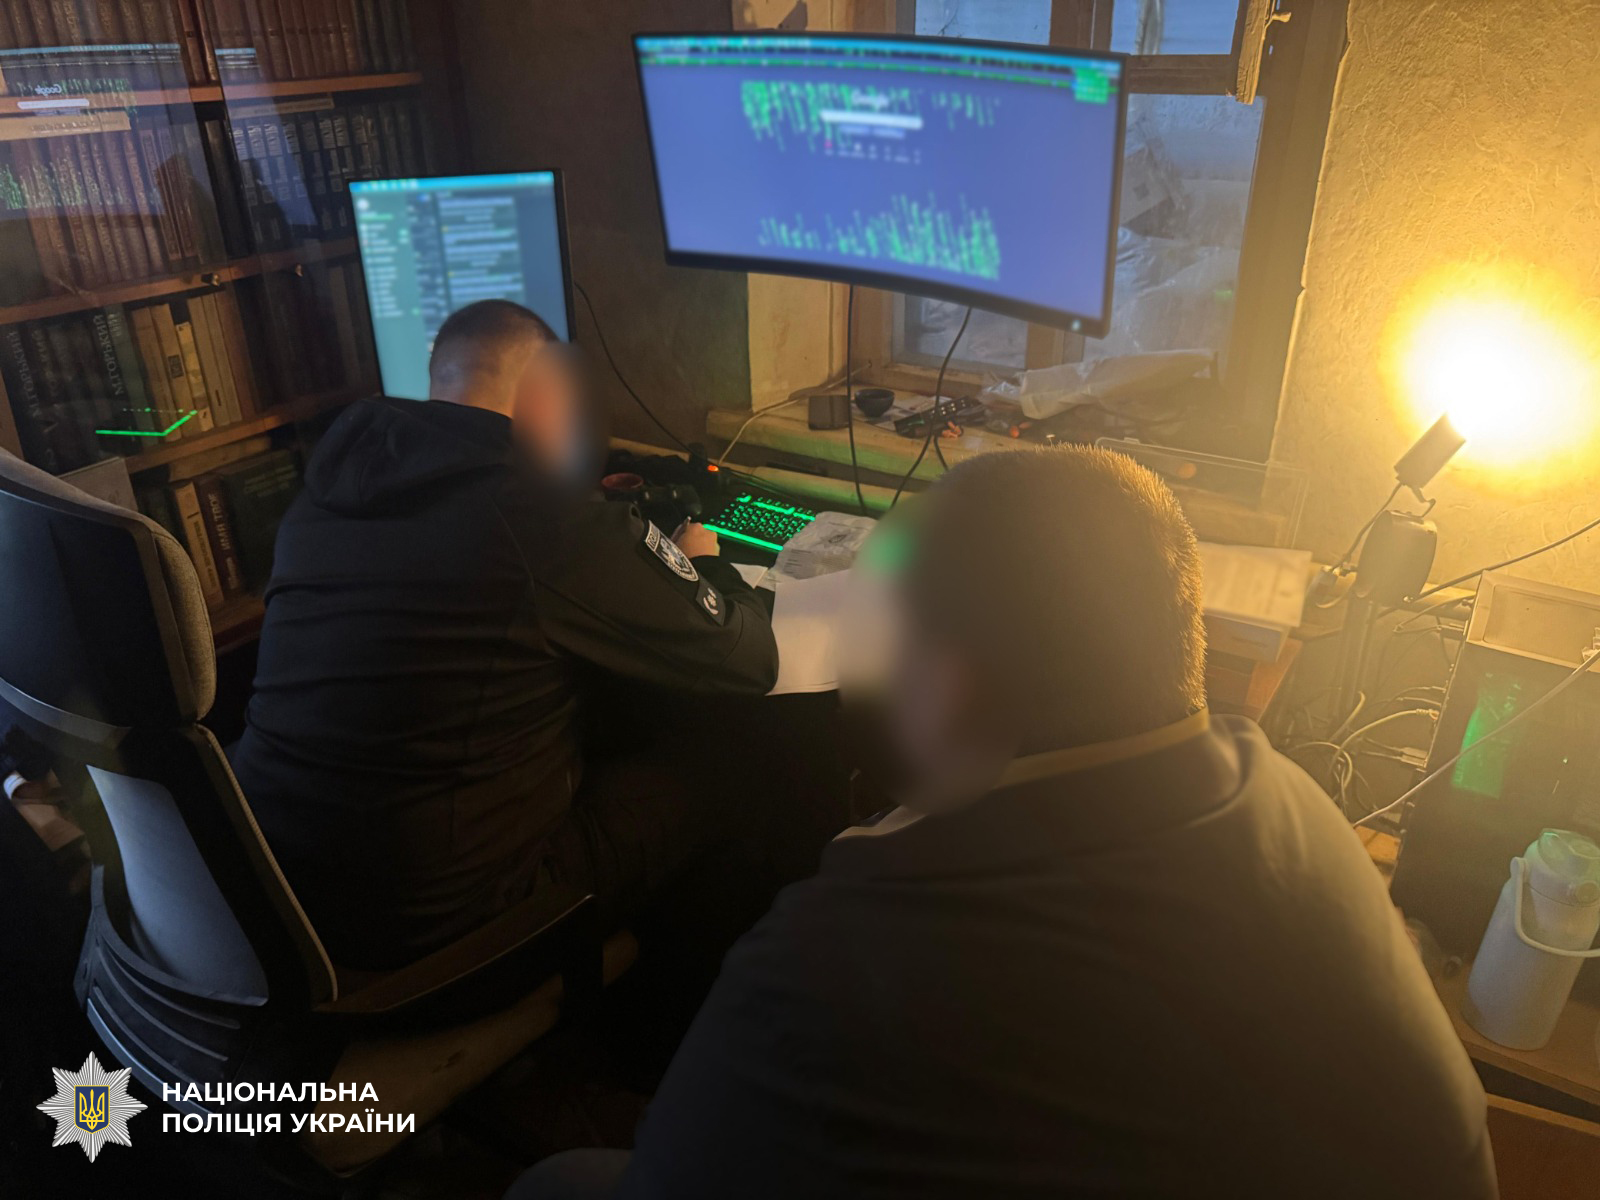
У межах міжнародної операції поліцейські за процесуального керівництва Офісу генерального прокурора провели 66 одночасних обшуків у Києві та 11 областях України. До заходів залучили представників правоохоронних органів США. Силову підтримку забезпечували бійці спецпідрозділів, зокрема TacTeam у Києві.
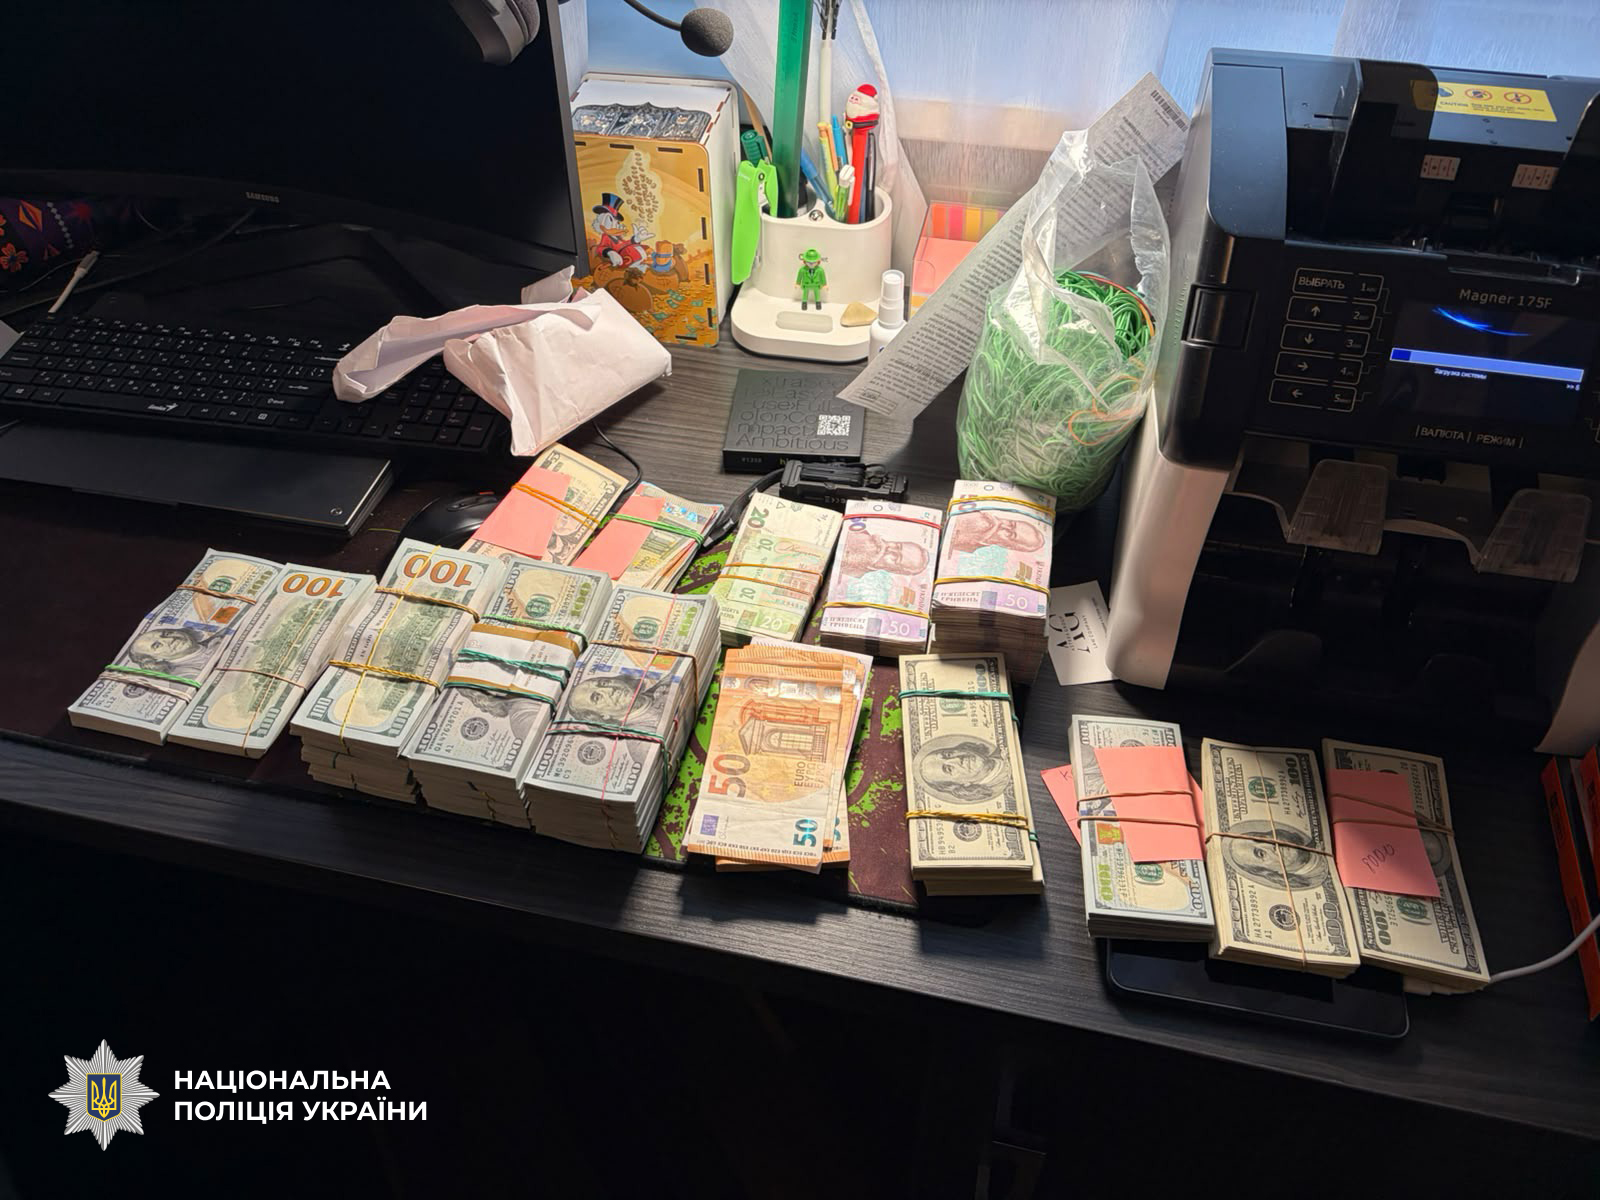
Вилучили комп’ютерну техніку, телефони, банківські картки, майже 370 тисяч доларів та 20 тисяч євро готівкою.
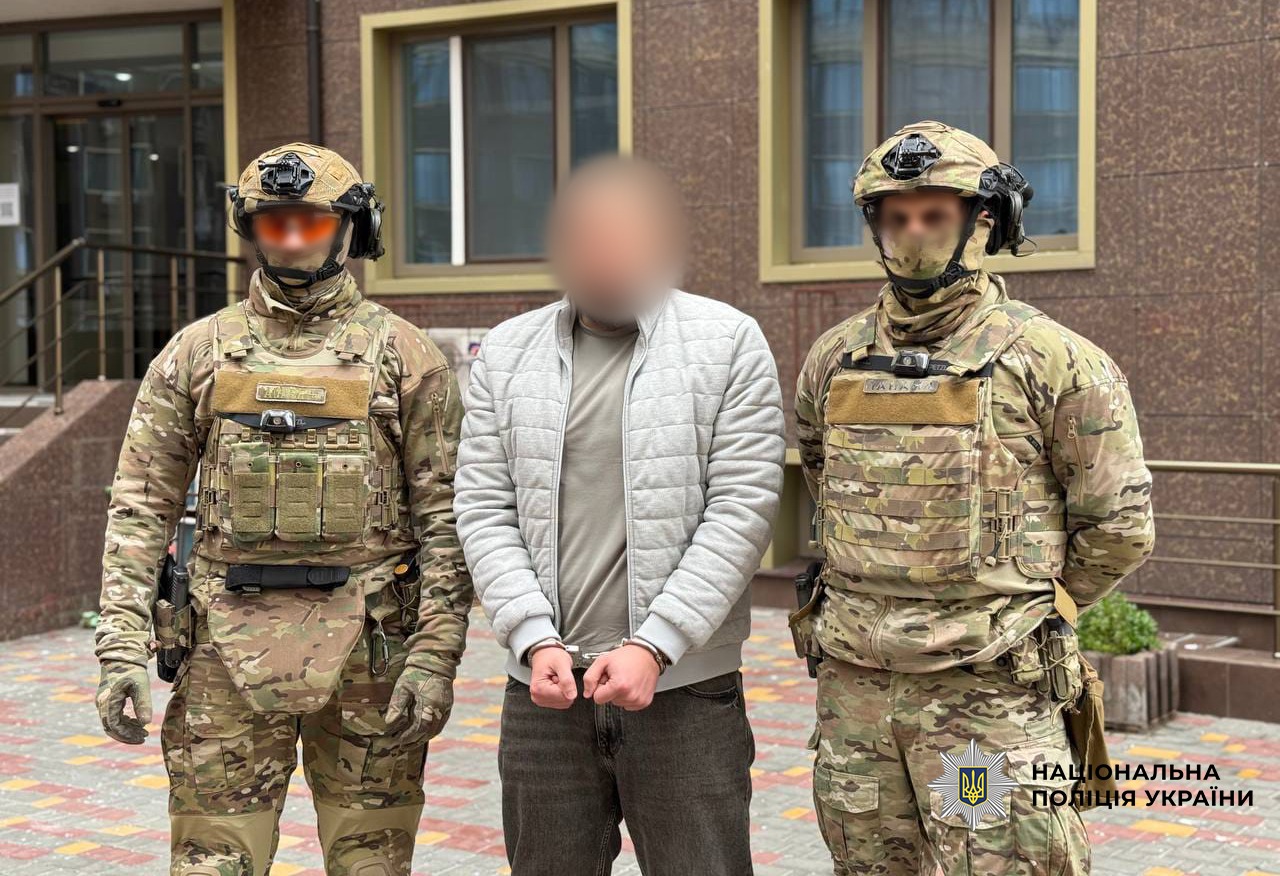
«Чотирьом ключовим учасникам угруповання повідомили про підозру. Усі четверо перебувають під вартою. Продовжуємо встановлювати інших учасників міжнародної мережі та їхню причетність до атак», — повідомив Цуцкірідзе.
Підозри стосуються участі у злочинній організації та несанкціонованого втручання в роботу інформаційних систем — ч. 2 ст. 255 та ч. 5 ст. 361 Кримінального кодексу України. Підозрюваним загрожує до 15 років позбавлення волі.
за матеріалами Головного слідчого управління та Кіберполіції НПУ
________________________________________________________
A Call from “IT Support” Leaves a Company at the Mercy of Hackers: National Police Chief Reveals Details of Cybercriminal Gang That Made Over $40 Million
An employee of a company was speaking on the phone with someone posing as an IT support specialist. While one criminal kept the employee on the line, another was accessing the company’s corporate systems. The call ended only after the successful breach had been confirmed. This was one of the documented episodes in the activities of an international hacking group that stole data, disrupted business operations and demanded multi-million-dollar ransoms.
Acting Head of the National Police of Ukraine Maksym Tsutskiridze spoke to Censor.NET in an exclusive interview about the joint investigation conducted with the FBI. Among the victims was a US company that paid the hackers five million US dollars following an attack.
“The attackers stole 1.4 terabytes of data from a US company and extended the attack to other companies within the same corporate group. Initially, they demanded $10 million. Following negotiations, they received $5 million,” he said.
The activities of the criminal organisation were documented for more than two years by officers of the Cyber Police Department and investigators of the Main Investigation Department, in cooperation with the US Federal Bureau of Investigation (FBI).
“We have identified at least 28 companies that transferred more than $40.5 million in ransom payments to the hackers, equivalent to approximately UAH 1.8 billion. This is money that has already been paid. We are still establishing the full extent of the damage,” Tsutskiridze noted.
According to the investigation, the organisation comprises at least 27 individuals from various countries, including Ukraine, Kazakhstan and Russia. A wider criminal network associated with it has more than 60 members operating across eight jurisdictions. Some of them are former members of the notorious Conti hacking group.
Each attack was carefully planned. The criminals examined the target company’s financial standing, assets, employees and vulnerabilities in its information systems. Their targets included companies in the oil and gas, pharmaceutical, industrial and logistics sectors, financial institutions and critical infrastructure facilities.
To gain access to corporate networks, the attackers used social engineering techniques to deceive employees. According to the Head of the National Police, the group had developed its own tool to automate such interactions.
“They created their own platform featuring voice messages generated by artificial intelligence. They called company employees, posing as IT support specialists. Under the pretext of providing technical assistance, they persuaded employees to disclose their login credentials or install remote access software. This allowed them to gain access to corporate networks,” Tsutskiridze explained.
Once inside the networks, the hackers stole confidential information and encrypted files, including through the use of ransomware. As a result, companies were unable to continue their normal operations.
“They would deprive a company of access to its own data and then demand millions of dollars in exchange for decrypting it. At the same time, they threatened to publish the stolen information. Victims were put under pressure from both sides, forcing them to pay the ransom in cryptocurrency,” he explained.
As part of the international operation, police officers, under the procedural supervision of the Office of the Prosecutor General, conducted 66 coordinated searches simultaneously in Kyiv and 11 regions of Ukraine. Representatives of US law enforcement agencies also took part in the operation. Tactical support was provided by special police units, including TacTeam in Kyiv.
Investigators seized computer equipment, mobile phones, bank cards, nearly $370,000 and €20,000 in cash.
“Four key members of the group have been formally notified of suspicion. All four are in custody. We continue to identify other members of the international network and establish their involvement in the attacks,” Tsutskiridze stated.
The charges concern participation in a criminal organisation and unauthorised interference with the operation of information systems, under Part 2 of Article 255 and Part 5 of Article 361 of the Criminal Code of Ukraine. The suspects face up to 15 years of imprisonment.
based on information from the Main Investigative Directorate
and the Cyber Police of the National Police of Ukraine